
Datris Frames Its AGPL Stack as a Data Control Plane for MCP Agents
On September 22, 2026, Datris.ai announced a major update to datris-platform-oss under AGPL-3.0—credential brokering via Vault, isolated tap execution, per-action Agent Policy, audit logging, row-level provenance, and an optional recovery agent for self-hosted MCP data work.
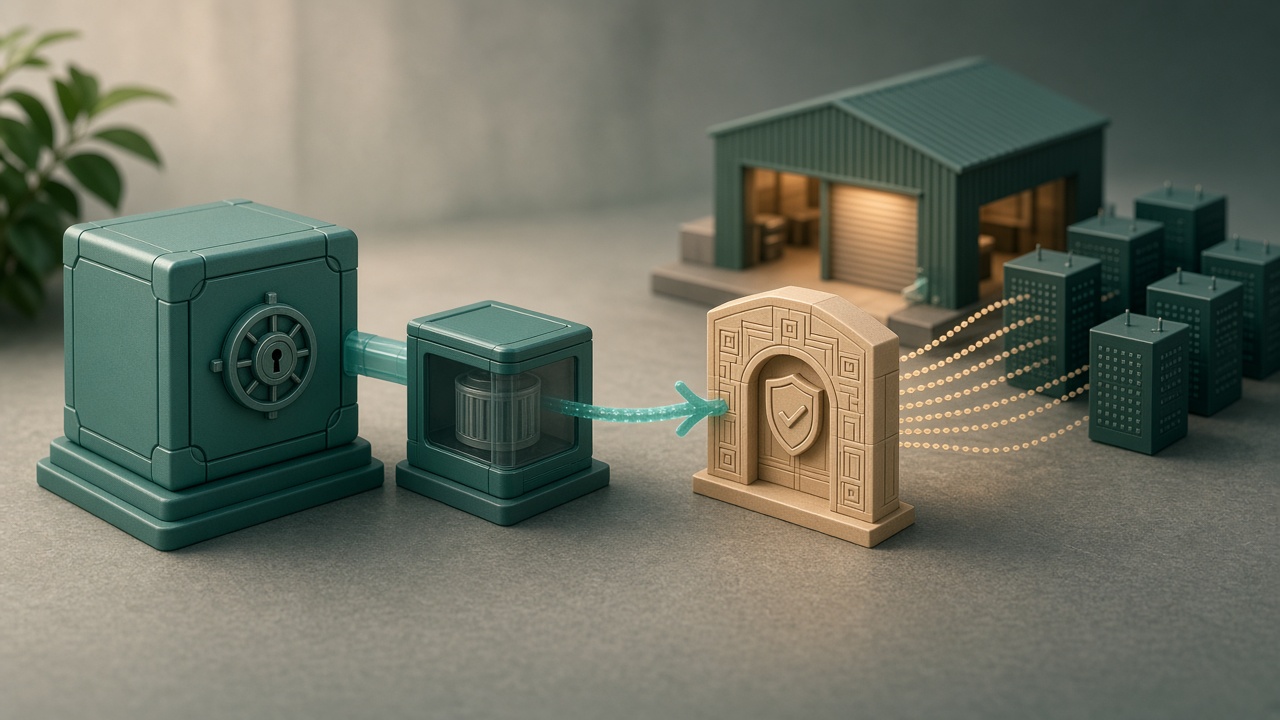
Datris.ai announced on September 22, 2026 a major update to its self-hosted open-source platform, which the company now describes as a data control plane for AI agents rather than only a pipeline toolkit. The company release says the drop adds credential brokering, isolated script execution, per-action policy, audit logging, row-level provenance, and an automated recovery agent so Model Context Protocol (MCP) clients can acquire, validate, and land production data without holding secrets or running unsupervised code on the host. Source is published at datris/datris-platform-oss under AGPL-3.0; Datris says it does not operate a managed service and collects no product telemetry.
Datris first shipped the platform in April 2026 for agents that build and operate data pipelines over MCP. Founder Todd Fearn’s company statement frames the September update as the production hardening pass: after showing an agent could run the full data loop, the harder problem is treating the agent as an identity that must be scoped, code that must be contained, and an actor that must be accountable. That pitch matches what enterprise data teams usually ask when coding agents start touching warehouses—who ran which script, which key allowed it, and whether a prompt can override policy.
Governance surfaces that are platform-enforced
According to the September 22 release and Datris’s security page, all capabilities sit behind a single MCP server. Each agent connects with its own key and sees only the tools that key permits. Agent Policy, described as opt-in in product docs and highlighted in the release, sets per-action rules—allow unattended, require human approval, or refuse—for operations such as running taps, deleting pipelines, or writing secrets. Policy is enforced by the platform rather than by prompt text, and it applies to both the built-in Assistant and external MCP clients such as Claude, Cursor, or other compatible hosts.
Credentials are referenced by name and resolved through HashiCorp Vault at run time. Agents never receive the secret values in configs, prompts, or chat history. Agent-written tap scripts run in a separate sidecar container with no platform secrets inside and no network route to the platform database, object store, or Vault; Docker Compose defaults documented in the changelog turn that isolation on via USE_TAP_RUNNER. Teams that refuse to run generated Python on the platform can instead host HTTP taps as their own services so Datris only pulls records.
Audit logging attributes creates, changes, runs, deletes, logins, and denied requests to human logins or agent API keys, with CSV export and SIEM mirroring called out in the release. When provenance is enabled for a pipeline, each landed row, document, and vector chunk is stamped with run, script commit, pipeline version, and source identifiers so a single lookup can resolve origin—useful when RAG answers need citations that survive chat truncation. Lineage views trace source to tap to pipeline to dataset, and agents can search datasets by meaning through documented discovery tools.
Recovery, destinations, and how far the claims go
The recovery agent opens incidents when feeds fail repeatedly, loads error, or volumes swing unexpectedly, then diagnoses and either proposes or applies a narrow repair that must prove itself with a clean run or be reverted. Datris says recovery is disabled by default—an important detail for operators who do not want autonomous mutation of production pipelines. Destination coverage listed in the release includes Snowflake and Databricks alongside PostgreSQL, MongoDB, S3 Parquet/ORC, message queues, and five vector databases. Model providers named include Anthropic, OpenAI, Azure OpenAI, Amazon Bedrock, xAI, and local Ollama, with bundled embeddings for air-gapped installs.
The public GitHub README currently advertises on the order of seventy-plus MCP tools (badges and docs also mention mid-70s counts as the catalog grows), Docker one-line installers, a UI on port 4200, an API on 8080, and an MCP SSE endpoint on 3000. License verification is straightforward: the repository LICENSE file is the full GNU Affero General Public License v3 text, and the README badge matches AGPL-3.0. Commercial licenses with support are offered separately; Datris says commercial and open-source builds are identical.
Treat performance, “production-ready,” and competitive positioning language as vendor narrative. What is grounded for this package is the September 22 company disclosure, the AGPL-3.0 LICENSE on GitHub, the documented Vault/isolation/policy/audit/provenance model on datris.ai/security and docs.datris.ai, and the explicit self-hosted / no-managed-service posture. Operators evaluating the release should start from the Docker installer or clone, enable Agent Policy and audit logging deliberately, keep recovery off until they understand repair scope, and remember AGPL-3.0 network-copyleft obligations if they modify and offer the software as a service to others.
- #AI Agents
- #Opensource

Author
Raj M
Contributor
AI Systems Architect is a seasoned technology leader with over 15 years of experience in the IT industry working with Fortune 500 companies. With a solid foundation in multi-agent systems, open-source LLM infrastructure, and enterprise deployment, he excels at building scalable production-grade AI platforms.