
OpenAI Expands Daybreak Program with Dual Access Tiers and Releases GPT-5.6-Cyber Model
On August 10, 2026, OpenAI announced the expansion of its Daybreak cybersecurity initiative, introducing two access tiers—Daybreak Blue and Daybreak Red—alongside a specialized cybersecurity model named GPT-5.6-Cyber. The program provides approved security researchers with access
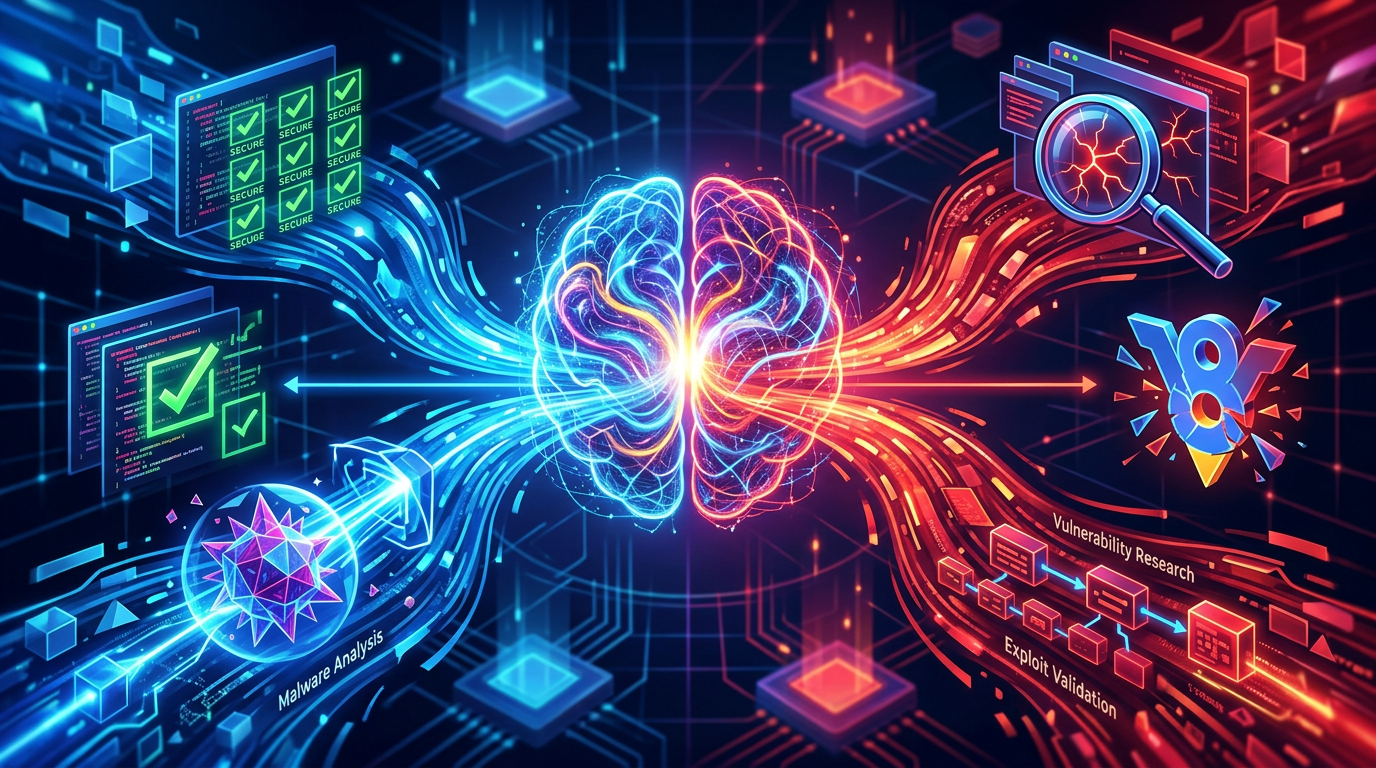
On August 10, 2026, OpenAI announced the expansion of its Daybreak cybersecurity initiative, introducing two access tiers—Daybreak Blue and Daybreak Red—alongside a specialized cybersecurity model named GPT-5.6-Cyber. The program provides approved security researchers with access to frontier intelligence, reduced refusal rates on technical tasks, and modified guardrails for legitimate defensive operations.
Program Structure and Access Tiers
OpenAI divided the Daybreak program into two operational access tiers designed for approved security organizations and vetted researchers. Access to both tiers requires identity verification, account security checks, legal attestations, and ongoing monitoring.
The two tiers provide distinct model access levels based on defensive security roles:
- Daybreak Blue: Provides access to general-purpose frontier models, including GPT-5.6 Sol, with safety guardrails adjusted for authorized defensive security tasks. Supported use cases include secure code review, vulnerability discovery, malware analysis, incident response, and patch validation.
- Daybreak Red: Provides access to purpose-trained cybersecurity models, including GPT-5.6-Cyber, for authorized vulnerability research, exploit validation, and red teaming.
According to the company, standard production models deploy system-level screening guardrails that can inadvertently block legitimate security work. Daybreak Blue removes those system-level filters, while Daybreak Red delivers a dedicated model trained to process dual-use prompts without triggering standard refusals.
GPT-5.6-Cyber Performance and Benchmark Results
GPT-5.6-Cyber is built on the architecture of GPT-5.6 Sol and specifically trained to handle complex cybersecurity tasks. The model reduces prompt refusals while improving task execution in zero-day discovery and exploit development.
To measure refusal rates on complex requests, OpenAI conducted an internal evaluation called the Advanced Cybersecurity Completion Rate. This evaluation tests model responses to prompts involving authentication bypass, privilege escalation, and exploit-chain development.
Model completion rates across tested configurations were:
- GPT-5.6-Cyber (Daybreak Red): 95.0% completion rate.
- GPT-5.5-Cyber (Daybreak Red): 57.3% completion rate.
- GPT-5.6 Sol (Daybreak Blue): 2.0% completion rate.
- GPT-5.6 Sol (Standard Safeguards): 1.5% completion rate.
Across technical capability benchmarks, model performance varied by task type. On ExploitGym2, which measures an agent’s ability to turn known vulnerabilities into working exploits inside isolated environments, GPT-5.6-Cyber outperformed both GPT-5.6 Sol and GPT-5.5-Cyber.
On internal zero-day discovery tests using open-source code repositories, GPT-5.6-Cyber under Daybreak Red produced higher-rated proof-of-concept exploits and technical write-ups than GPT-5.6 Sol under Daybreak Blue. On the Vulnerability Discovery and Report Writing evaluation, GPT-5.6-Cyber scored lower than GPT-5.6 Sol due to producing shorter, less detailed report outputs. On ExploitBench, which evaluates developing a V8 vulnerability into a full exploit, GPT-5.6 Sol under Daybreak Blue showed higher token efficiency and accuracy over 300 turns, though the performance gap between the models narrows when extended to 600 turns.
Real-World Software Vulnerability Findings
OpenAI applied GPT-5.6-Cyber to identify novel software vulnerabilities across several major open-source and commercial software projects prior to the model’s public announcement.
In Chrome’s V8 JavaScript engine, the model uncovered two unknown vulnerabilities that could be combined to corrupt memory and escape the V8 heap sandbox. OpenAI reported the findings through coordinated vulnerability disclosure, leading Google to release a fix for the bug, designated as CVE-2026-15903. The bug involved an optimizing compiler error in V8 that omitted integer conversion safety checks, allowing out-of-bounds memory access.
The model also identified vulnerabilities in several other software systems:
- At least five vulnerabilities in a popular mobile operating system, including a local privilege escalation exploit chain.
- Three critical vulnerabilities in a popular database software, including a remote code execution vector.
- Over 400 privilege escalation vulnerabilities in an operating system kernel.
OpenAI stated that it is coordinating remediation efforts for these remaining issues alongside partner organizations and open-source software maintainers.
Safety Ratings, Early Deployments, and Security Mandates
Under OpenAI’s internal Preparedness Framework, GPT-5.6-Cyber received a “High” cybersecurity capability rating, which sits below the “Critical” classification threshold. The announcement noted that GPT-5.6-Cyber was not involved in the recent Hugging Face security incident.
Early access was granted to enterprise security partners, including SpecterOps, Palo Alto Networks, CrowdStrike, Cisco, Cloudflare, Fortinet, and Sophos.
“[GPT-5.6 Cyber] is materially improving our specialist vulnerability-research workflows: it reasons more accurately about real exploit constraints, tracks complex state better, and has completed work in under a day that earlier models had not resolved after weeks of intermittent effort.” — Jared Atkinson, CTO of SpecterOps
OpenAI announced new security requirements for organizations participating in Daybreak. Beginning September 1, 2026, all individual accounts with Daybreak access must use hardware security keys. OpenAI is also encouraging Codex users to switch to auto-review mode, which evaluates agent tool calls outside the sandbox environment before execution.
Recommended practices for participants include:
- Sandboxing all workflows in controlled environments isolated from sensitive production systems and the public internet.
- Enabling auto-review mode and configuring custom permission policies for automated tool calls.
- Defining explicit permission boundaries and profile limits for cybersecurity tasks.
- #Opensource

Author
Krishnan
Contributor
Enterprise Technology Explorer is a business and operations professional with over 15 years of experience across multiple industries working with Fortune 500 companies. With a solid foundation in enterprise processes, digital adoption, and technology evaluation, he excels at bridging business needs with emerging technologies to build scalable enterprise-grade applications.